Career
I've spent more than fifteen years in security engineering, most recently using AI where it genuinely helps.
-
Meta Privacy Engineer
I was key to PrivacyBrain, an LLM derived from Llama that evaluated privacy incidents, reviews, and FTC commitments across hundreds of millions of records, and Project Terminus, which linked incidents to their root causes and replaced months of manual investigation with consistent automation. I also wrote an LLVM-bitcode scanner (PSAPI) for sensitive iOS and macOS APIs and contributed to the design of Llama 4.
Coinbase Security Architect
-
Dropbox Senior Security Engineer
I worked on corporate authentication, key management and Windows security in the datacenters, and open-sourced efivalidate for checking Mac firmware.
Uber Advanced Technologies Group Senior Security Engineer
-
Jet.com Senior Software Security Engineer
I was the company's first security engineer, securing what was then the largest e-commerce site on Azure.
-
Bloomberg Senior Web Application Developer
On Bloomberg's legal research platform.
-
Microsoft Software Engineer, then Azure Security SDE II
I did threat modeling and penetration testing for Azure, automated security health reporting across more than 150 teams, and worked on the Windows Data Classification Toolkit. I hold a patent on detecting and preventing phishing attacks.
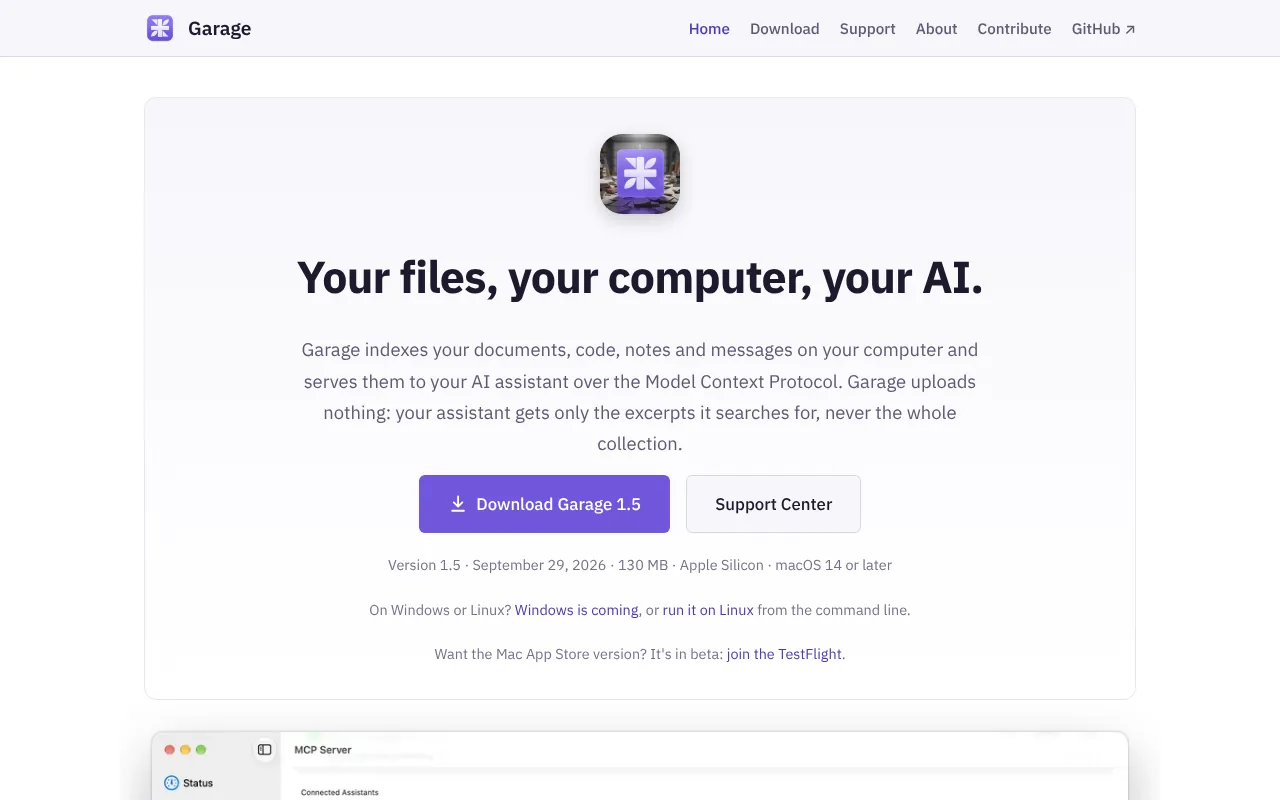
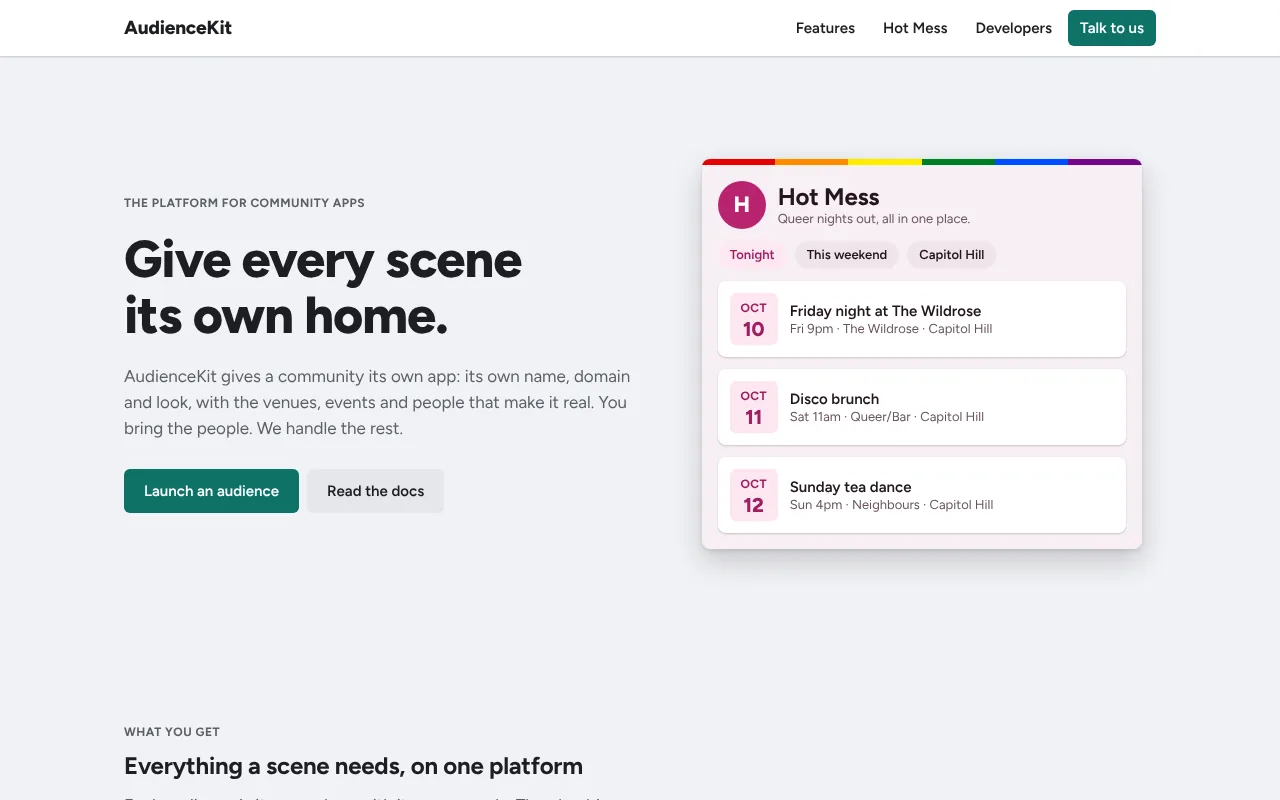
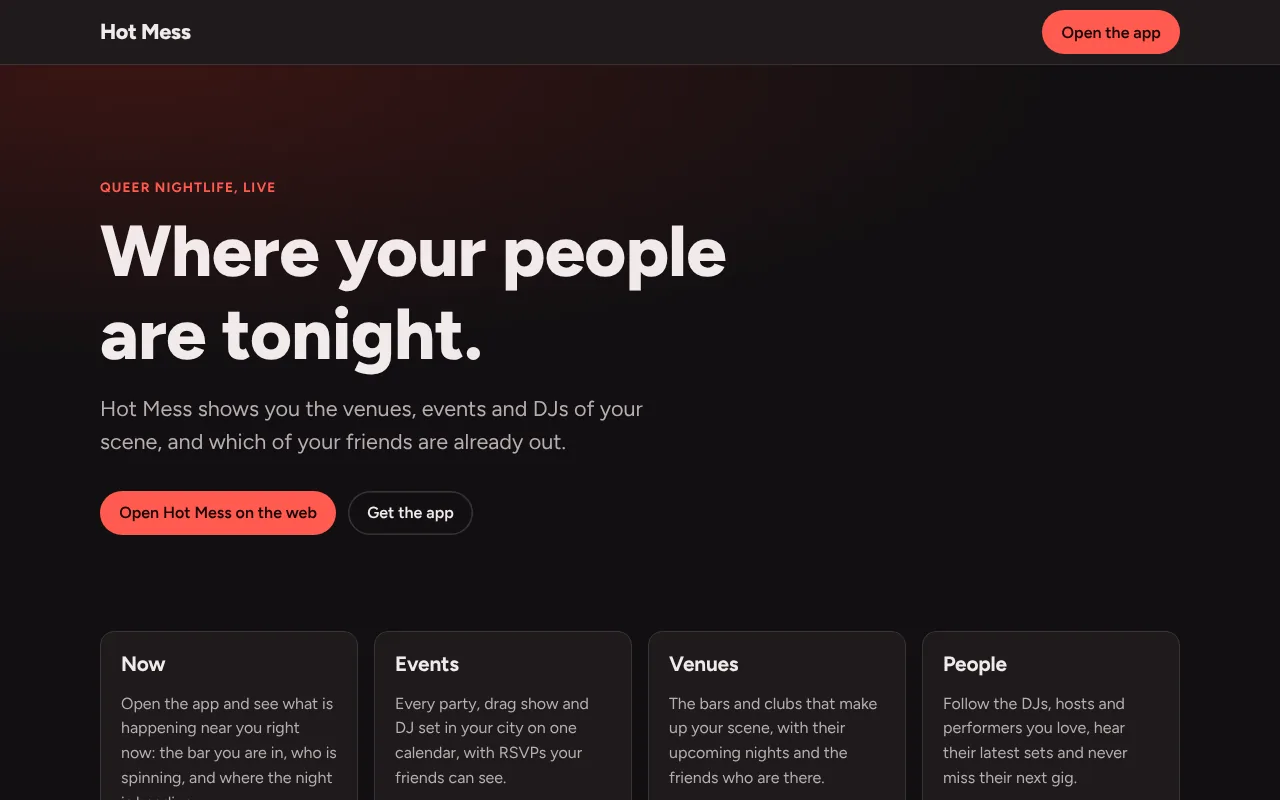
I also founded Hot Mess and AudienceKit, products that apply social science to in-person community, and I build Garage. They're below, with more on the Products page.
Apple security research
I'm best known for research into Apple's T2 security chip as part of Team t8012.
- 2017Built an early T2 integrity verification tool.
- Oct 2019Proposed that the checkm8 bootrom exploit reached the T2, and extended ipwndfu for it.
- 2020Performed the team's first successful SecureROM dump.
- 2020Helped bring the exploit into the checkra1n jailbreak.
- 2020Adapted libimobiledevice to talk to the T2, and reverse engineered the USB Target Disk Mode protocol.
When the research went public in October 2020, I explained to the press, including Forbes and The Register, why the flaw can't be patched in shipping Macs.
I'm part of Hack Different, an open-source community around Apple platforms. There I maintain apple-knowledge, a machine-readable collection of reverse-engineered Apple hardware and software facts, and my most widely used project, with over 1,400 stars on GitHub. I also contribute to The Apple Wiki.
Research and open source
Most of my work is on GitHub. Beyond the T2, it falls into a few areas. My current working papers are on the Research page.
Firmware and boot security
- mojo_thor 2017 research into malware that infects the EFI and SMC firmware of MacBooks
- peiutil 2017 converts UEFI PEI images (TE and VZ files) to PE, so they can be disassembled
- apple_ssv 2020 explores macOS Signed System Volumes
- windows-bluepill 2022 looks at breaking a system's security without breaking Secure Boot
Ports, cables, and radios
- badusb 2019 detects and exploits time-of-check/time-of-use gaps in USB mass storage
- lightning_strike 2019 and lightning_dfu 2021 study the security of the Lightning connector
- apple_utdm 2020 a Linux kernel driver for Apple's USB Target Disk Mode
- apple-malicious-baseband 2022 documents a malicious cellular baseband image that carried Apple's signature
Libraries for Apple formats and services
- libapfs for the Apple File System
- pyxar for XAR archives
- libiupdate for Apple software updates
- libicloud for iCloud
- apple_net_recovery for Internet Recovery
- libidevice and libxpc, Rust reimaginings of libimobiledevice and XPC
Tools that protect people
- isafety 2020 examines iPhones and iPads for security and safety threats
- chainfix 2024 checks and repairs Keychain and iCloud Keychain
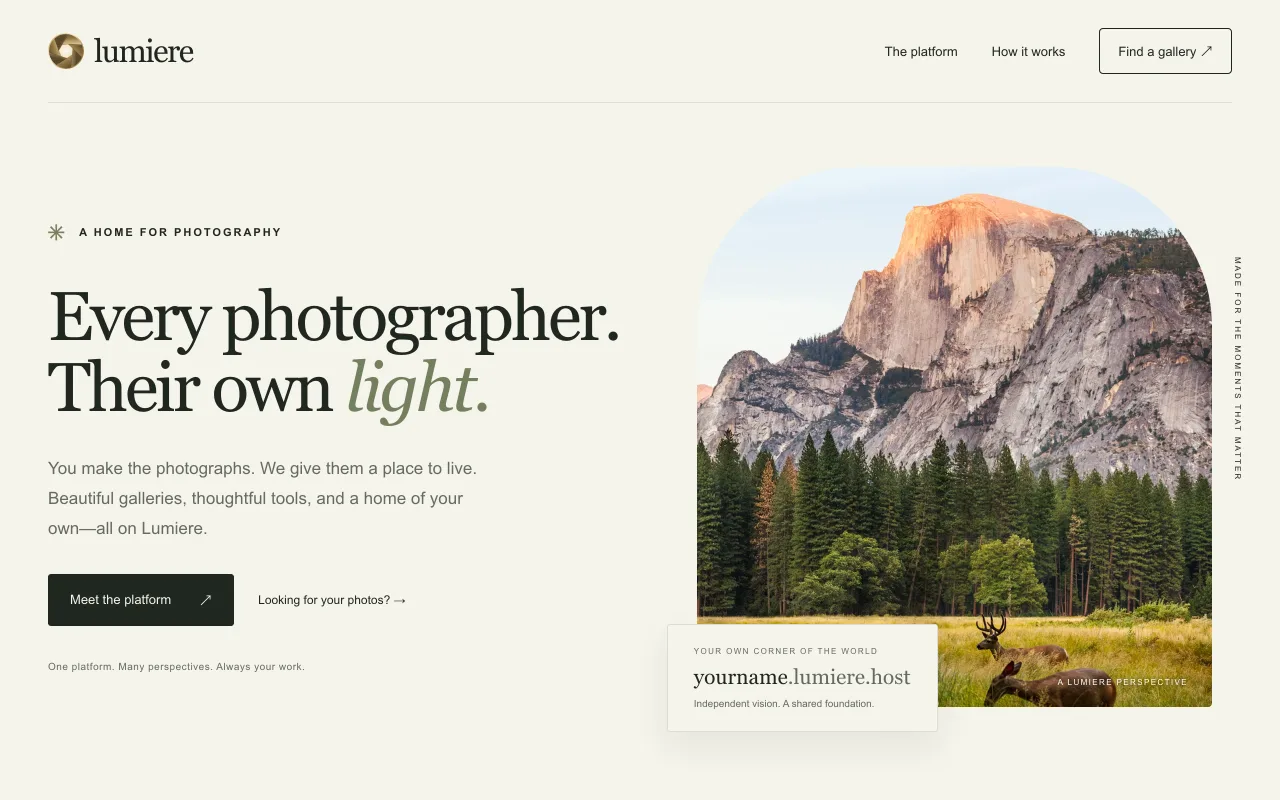
- Lumière Archive (hedonism_bot) gives every photographer their own gallery at lumiere.host or on their own domain, a living portfolio that uses Postgres, pgvector and embeddings to group faces without naming anyone, so people can find the photos they appear in and order prints
- meshtastic-map-manager manages Meshtastic map data
In the organizations I run
I also own the Hack Different and Team t8012 organizations on GitHub. Besides apple-knowledge, their projects include:
- webmuxd and go-webmuxd, a proof of concept of an attack where a browser may be able to access iPhone sync data
- demuxusb, a tool to decode iDevice USB capture sessions
- smcutil, a decoder for Apple's SMC payloads (T1 and prior)
- efivalidate for validating the firmware of Macs up to the T1
- libapplefw, generic utilities for Apple firmware images
- go-aapl-integrity and cnklverify for Apple's integrity formats (img4, chunklists, trust caches)
- secure_emu, which runs portions of SecureROM under the Unicorn emulator
- mootool, generic parsing of Apple security state information including LocalPolicy, FDR, signed APTickets, and more
- yolo_dsc for extracting the dyld shared cache
- symbol-server for annotating Apple symbols
- xnudex for indexing XNU OS images
- kext-kmem, a kernel extension for reading and writing kernel memory, replacing /dev/kmem
- homebrew-jailbreak, a Homebrew tap of research tools
- newosxbook-tools, which packages Jonathan Levin's tools for it
- libibackup for iOS backups
- apple-diagnostics-format for Apple's wireless diagnostics files
- apple-baseband for the modem baseband
- uarp for Apple's accessory firmware update protocol
- pongo-flash, from the T2 work, a flash storage driver for checkra1n's pongoOS
- RemoteServiceDiscovery, from the T2 work, a reverse-engineered rewrite of Apple's framework of that name
Contributions to other projects
I've had pull requests merged in more than 25 projects outside my own. Among them:
Apple platform tooling
Mach-O fileset support and new segment types in Homebrew's ruby-macho (five merged PRs), T2 support in usbmuxd, Linux fixes to ipwndfu, build work on checkra1n's PongoOS, pkg-config support in ldid, the convert verb in dmglib, and firmware sources in Acidanthera's MacInfoPkg.
Reverse engineering
Universal macOS builds of the Capstone disassembler, a fix to Vector 35's Objective-C workflow for Binary Ninja, and an easier install for MEAnalyzer, Intel's Management Engine analyzer.
Security
OpenSSL::BN#abs in Ruby's openssl library, removing unsafe OpenSSL patches from money-tree, and a stricter content security policy for Dropbox's merou permissions system.
Data and infrastructure
The build and validation tests for AppleDB (four merged PRs), universal macOS build instructions for Zstandard, fixes to Homebrew, overcommit and keccak.rb, and Meshtastic firmware dev containers.
SDR and ham radio
Ported bladeRF and libbladeRF, android-sdr-kit, and SDR++ to Android (#1063).
Work with me
I'm available for AI security, privacy engineering, and security research roles, remote or hybrid.
Get in touch on LinkedInSupport the work
If my open-source work is useful to you, you can support it on Patreon, or follow along on GitHub.
Outside of work
Away from the keyboard, I make documentary film and photography centered on the LGBT community.